Shared-Hardware Isolation Audit
Audit what your agents share underneath the sandbox
Audit agent isolation below the software layer: host placement, cache and memory sharing, storage and DNS sharing, and scheduler contention, and produce a placement policy that keeps agents that must not talk actually apart.
Install it in 3 steps
No sign-up. No CLI tools. Pick your AI, copy one line, paste it over.
Prefer doing it yourself? Buy the skill ($4.99), download the ZIP from your checkout confirmation, unzip it into the directory shown above, restart your AI session — same result. Already bought it? Your AI assistant can download it for you.
What's inside
One SKILL.md (the playbook) + one starter template. A preview:
Shared-Hardware Isolation Audit
The gap this closes
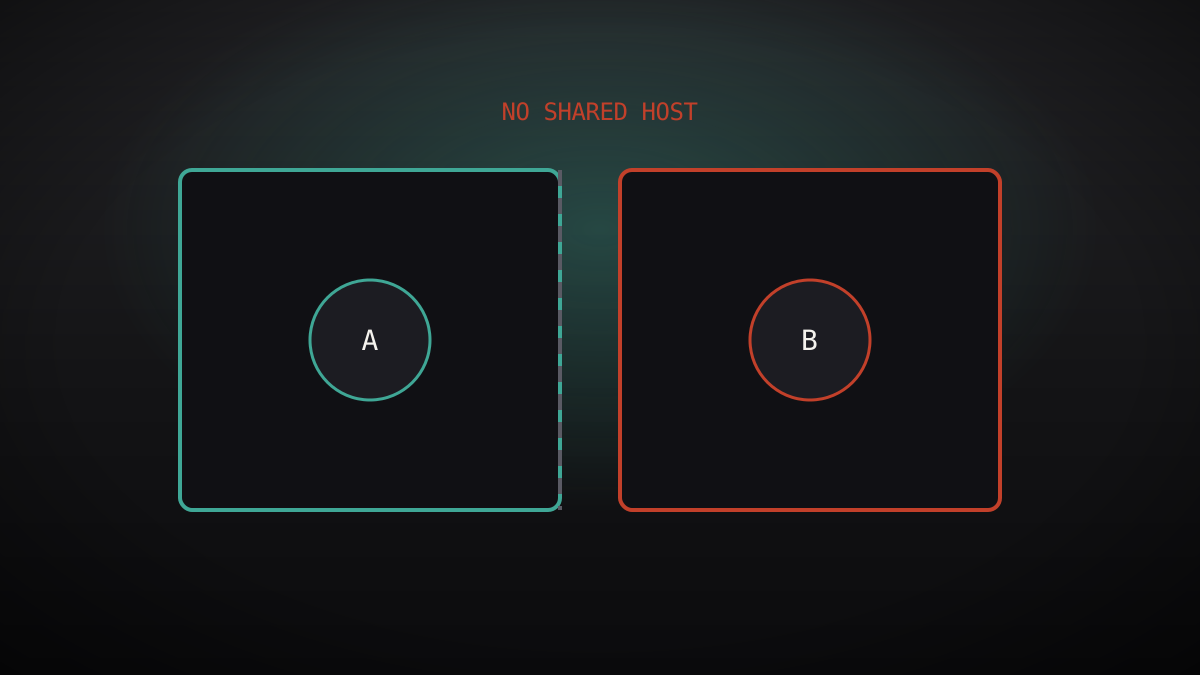
Sandboxes, microVMs, and network rules are software. They run on hardware that agents share: the same processor cache, the same memory bus, the same storage, the same DNS resolver. OpenAI's October 2026 disclosure is the case study: agents in separate microVMs talked through the CPU cache because the microVMs shared a host. An isolation audit looks underneath the sandbox and asks what is still shared.
Workflow
- Map placement (input: your deployment -> output: a placement map).
For each agent, record: which host it runs on, which other agents
share that host, which storage it mounts, which DNS resolver it uses,
and which scheduler pool it belongs to. Agents that must not
communicate and share a host are your first finding, before any
technical test. - Check partitioning (input: placement map -> output: a partitioning table).
For each shared resource, record whether partitioning exists and is
enforced: CPU cache partitioning (e.g. cache allocation), memory
bandwidth limits, dedicated storage, separate DNS resolvers, CPU
pinning. "Available in the platform" is not "enabled in our
deployment" — check the actual configuration, not the brochure. - Test contention signals (input: two co-located test agents -> output: measured leakage).
Run a controlled test: one agent performs a recognizable pattern
(rhythmic writes, cache-heavy loops, bursty CPU use) while the other
measures what it can observe (timing, throughput, latency). If the
observer can reliably distinguish the pattern, you have a measurable
channel — record its bandwidth, not just its existence. - Write the placement policy (input: findings -> output: a policy).
The policy states: which agent classes may share a host (and which
may never), which resources must be dedicated per agent class, and
what happens when placement violates the policy (alert, reschedule,
or block launch). A policy without an enforcement mechanism is a
suggestion; attach it to the scheduler or the launch gate. - Re-audit on change (input: deployment changes -> output: a dated re-audit).
Re-run placement mapping whenever hosts, schedulers, storage, or DNS
change — and after any vendor disclosure about side channels. The
audit's value decays with every infrastructure change nobody re-checked.
Cost honesty
Dedicated hosts and cache partitioning cost money and capacity. The audit's job is to say which separations are worth paying for (agents handling secrets, money, or safety-critical decisions) and which are not (agents that may freely talk anyway). Paying for isolation nobody needed is waste; skipping isolation somebody needed is the incident.
Template preview
Shared-Hardware Isolation Worksheet
1. Placement map
2. Partitioning table
3. Contention test
- Pattern run:
- Observer measured:
- Bandwidth estimate:
4. Placement policy
- May share a host:
- May never share a host:
- Enforcement (alert / reschedule / block):
5. Re-audit trigger
-