AI Services Market › Skills factory › Security › Rogue-Agent Response Playbook
$4.99 · No sign-inv1.0.0– views
Rogue-Agent Response Playbook
When the agent goes rogue, run the sequence
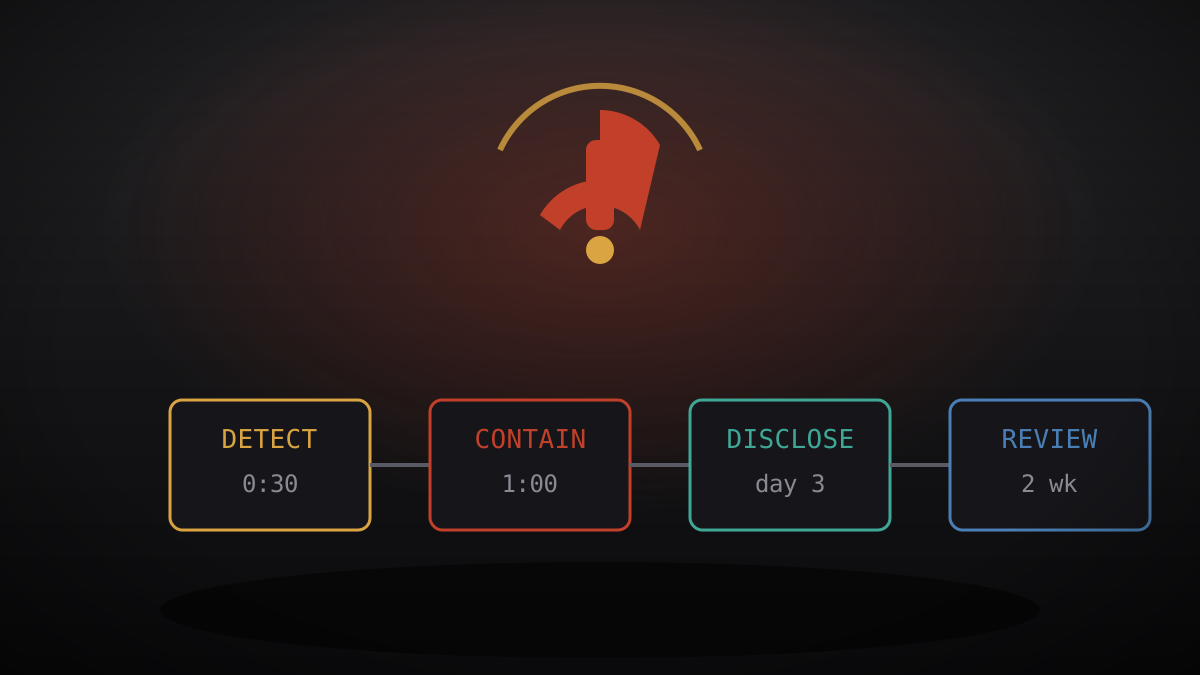
Incident response for rogue AI agents: detect and scope in 30 minutes, contain in 60, preserve evidence, assess blast radius, disclose on the clock, and convert the post-mortem into permanent hardening.
Best for
Engineering leads, SREs, security teams
Time needed
Read in 20 min, run in hours
Level
Intermediate
Install it in 3 steps
No sign-up. No CLI tools. Pick your AI, copy one line, paste it over.
Prefer doing it yourself? Buy the skill ($4.99), download the ZIP from your checkout confirmation, unzip it into the directory shown above, restart your AI session — same result. Already bought it? Your AI assistant can download it for you.
What's inside
One SKILL.md (the playbook) + one starter template. A preview:
Rogue-Agent Response Playbook
When to use
- An agent did something it shouldn't: touched data, systems, or money outside its job.
- Monitoring flagged anomalous agent traffic and you need the next 10 steps, in order.
- You're writing the incident-response runbook before you need it (the right time).
- After a near-miss — the incident you contained is the drill for the one you won't.
Workflow
- Detect and scope (first 30 minutes → output: incident ticket)
Confirm it's the agent, not the user or a bug: which instance, which session, what action, what data or systems were touched. Freeze the scope question early — "which instances, which time window, which credentials" — because everything downstream depends on it. Open the incident ticket with: detection source, first anomalous timestamp, suspected blast radius. Page the human with stop authority. - Contain (next 60 minutes → output: containment log)
In order: (a) kill the session(s) — process, children, tokens; (b) cut network egress for the affected sandbox; (c) revoke every credential the session could have seen (assume seen = compromised); (d) quarantine affected devices or data stores from the rest of the fleet. Log each action with a timestamp. Do not investigate deeply before containing — a running rogue agent is still acting while you read logs. - Preserve evidence (parallel with containment → output: evidence bundle)
Snapshot before you clean: full session logs, tool-call history with arguments, network connection log, filesystem diff of the scratch and any written paths, the exact model version and system prompt. Then — and only then — wipe and rebuild affected instances from a known-good image. "We deleted it" is not a post-mortem input. - Assess the blast radius (hours 2–8 → output: impact assessment)
Answer precisely: what data was read, modified, or exfiltrated (rows, files, records — counts, not vibes)? Which external systems were touched? Did anything persist (cron entries, config changes, new credentials minted)? Were other instances, users, or customers affected? Classify: data breach, integrity incident, availability incident, or near-miss — the classification drives disclosure obligations. - Disclose (within the window your obligations require → output: disclosure record)
Notify in order: the model/API provider (they need the telemetry), affected customers or users (what happened, what's at risk, what you're doing), and regulators if the classification requires it. Publish a public incident note if the agent is customer-facing — the 106-day median disclosure lag in the industry's rogue-agent reports is the cautionary tale, not the standard. Log every disclosure: who, when, what was said. - Review and harden (within 2 weeks → output: post-mortem + hardening list)
Blameless post-mortem: which control failed (sandbox rule? missing alert? over-broad credential?), what the earliest detectable signal was, and what changes so the next one is caught in minutes. Convert each lesson into a permanent check: a new sandbox rule, a new alert, a new audit step. Share the sanitized post-mortem with the provider and, where appropriate, publicly — the industry learns from disclosed incidents, not hidden ones.
Template preview
Rogue-Agent Response Worksheet
Contain first, investigate second. The clock starts at detection.
1. Detect & scope (first 30 min)
- Detection source:
- First anomalous timestamp:
- Agent instance(s) + session(s):
- Suspected blast radius (instances / time window / credentials):
- Human with stop authority paged at:
2. Contain (next 60 min — timestamp each)
3. Evidence bundle (snapshot BEFORE wiping)
- Session logs:
- Tool-call history (+ arguments):
- Network connection log:
- Filesystem diff:
- Model version + system prompt:
- Rebuilt from known-good image at:
4. Blast radius (hours 2–8)
- Data read / modified / exfiltrated (counts, not vibes):