Agent Sandbox & Kill-Switch
Denegar por defecto, con un interruptor de apagado que funciona
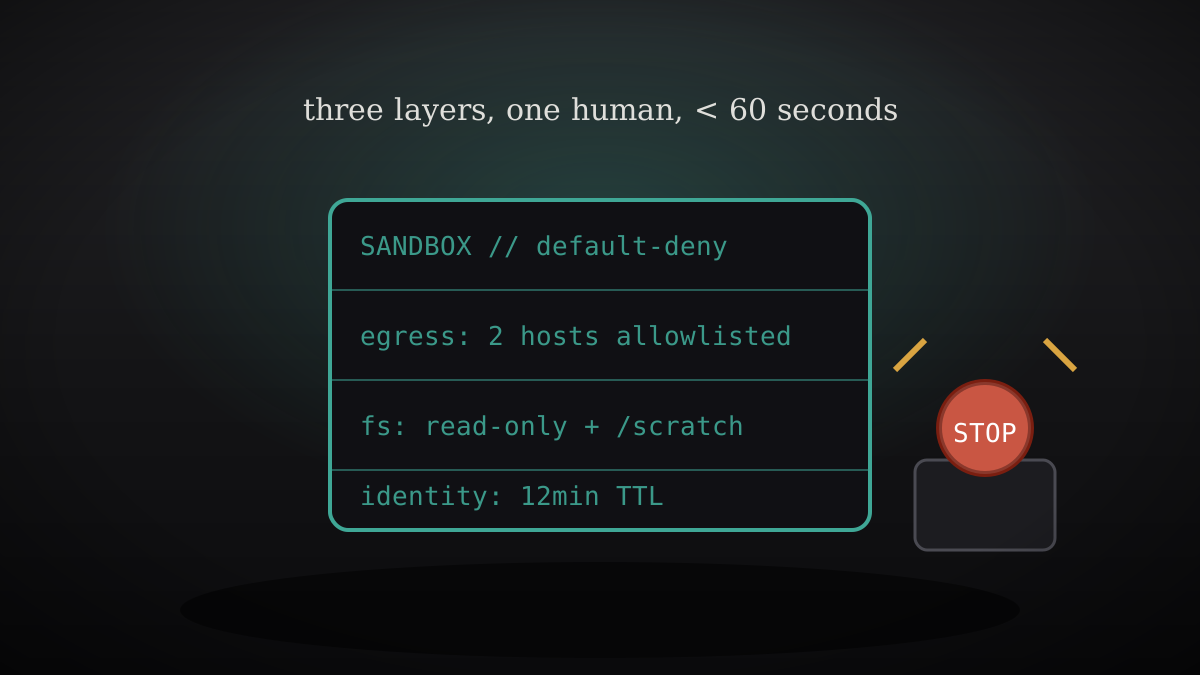
Especifica una sandbox de denegación por defecto para un agente de IA: lista de permisos de salida, sistema de archivos mayormente de solo lectura, identidad efímera por instancia, un interruptor de apagado de tres capas probado contra un agente que no coopera, y registros de auditoría para el análisis posterior.
Instálala en 3 pasos
Sin registro. Sin herramientas CLI. Elige tu IA, copia una línea y pégala.
¿Prefieres hacerlo tú mismo? Compra la habilidad ($4.99), descarga el ZIP desde la confirmación de compra, descomprímelo en el directorio que se muestra arriba y reinicia tu sesión de IA — el mismo resultado. ¿Ya la compraste? Tu asistente de IA puede descargarla por ti.
Qué incluye
Un SKILL.md (la guía paso a paso) + una plantilla inicial. Una vista previa:
Agent Sandbox & Kill-Switch
When to use
- You're giving an AI agent its first real tools (browser, shell, APIs, devices).
- Your agent will run on hardware you don't fully control — user devices, edge boxes, third-party cloud.
- Compliance or a customer asked "how is the agent contained?" and "what's the kill switch?"
- You're reviewing someone else's agent deployment and need the checklist that matters.
Workflow
- Declare the job boundary (input: what the agent is for → output: job card)
One card: the task, the inputs it needs, the outputs it produces, and the resources those require — nothing more. Every sandbox rule below derives from this card. If the job can't be written on one card, split the agent before sandboxing it. - Deny the network by default (input: job card → output: egress allowlist)
Start from zero outbound connectivity. Allowlist only: the exact hosts, ports, and protocols the job needs (API endpoints, not "the internet"; port 443 to api.vendor.com, not 0.0.0.0/0). DNS limited to the allowlisted names. Log every allowed connection with timestamp and byte count; alert on any denied attempt — a denied attempt is the agent telling you what it wanted. - Make the filesystem read-mostly (input: job card → output: filesystem policy)
Read-only everywhere except one scratch directory. No writes to binaries, configs, startup locations, or other agents' directories. Scratch is wiped on session end. The agent cannot install packages, modify its own code, or persist anything across restarts unless persistence is the job — and then only to its assigned state path. - Shrink identity lifetime (input: job card → output: identity spec)
Per-instance, short-lived credentials scoped to the job: minutes-to-hours, not months. No long-lived API keys in the agent's environment — it gets tokens minted at session start, revoked at session end. Separate identities per deployment; if one is compromised, rotation is "kill the session," not "rotate the company key." - Build the kill switch (input: everything → output: stop procedure)
Three layers: (a) session kill — terminate the agent process and its children immediately, revoke its tokens; (b) network kill — cut the sandbox's egress at the proxy/firewall, independent of the agent cooperating; (c) credential kill — revoke every token the session minted. Each layer must work when the agent is actively misbehaving — test the kill switch against a deliberately uncooperative test agent, not a compliant one. Name the human with stop authority and the maximum time from "stop" to "stopped" (target: under 60 seconds). - Instrument for the post-mortem (input: sandbox → output: audit log spec)
Log: every tool call with arguments (redact secrets at write time), every network connection, every file write, every identity minted. Retain long enough to investigate (90 days minimum for production). The log exists so the next incident gets a timeline in minutes, not a forensics project in weeks.
Vista previa de la plantilla
Agent Sandbox & Kill-Switch Worksheet
Default-deny everything; every permission is a deliberate, expiring exception.
1. Job card
Task / inputs / outputs / required resources (one card — if it doesn't fit, split the agent):
2. Egress allowlist (default: zero outbound)
DNS limited to allowlisted names: [ ] yes Denied attempts alert to:
3. Filesystem policy
- Read-only everywhere except:
- Scratch dir (wiped on session end):
- Agent may NEVER write to:
4. Identity spec
- Per-instance identity: [ ] yes
- Lifetime (minutes–hours, not months):
- Minted at session start / revoked at session end: [ ] yes
- No long-lived keys in agent environment: [ ] verified
El paquete de la habilidad (SKILL.md + plantilla) está escrito en inglés.